
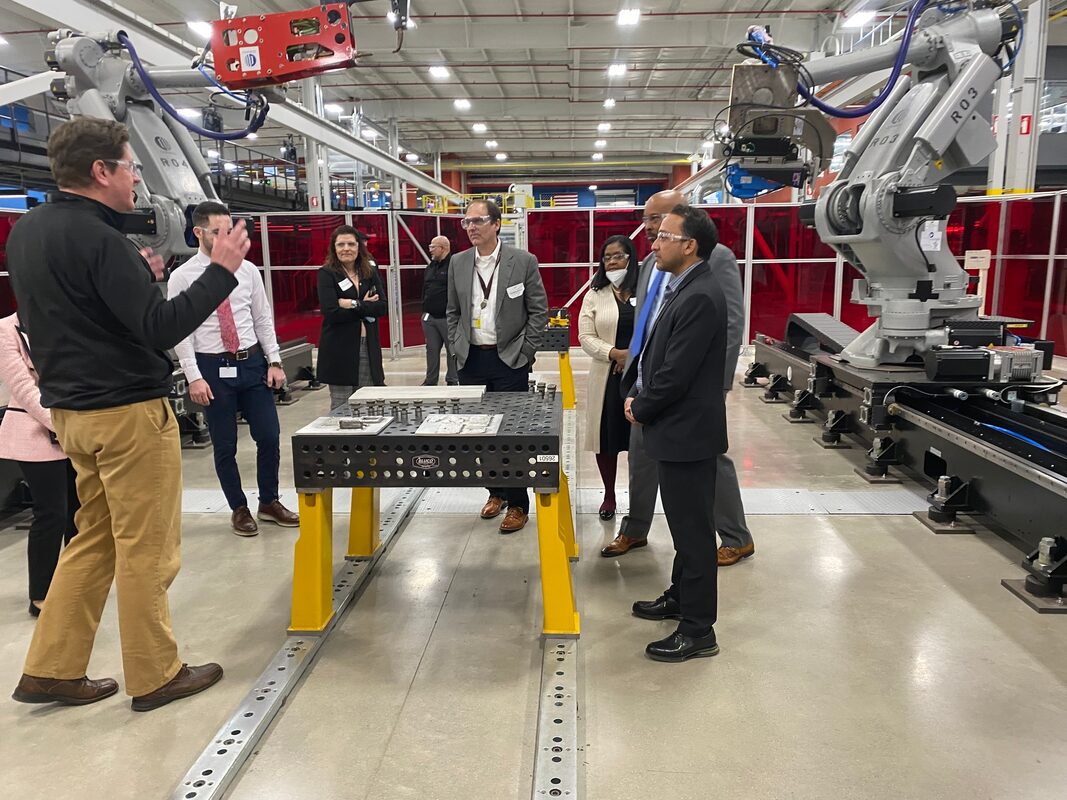
The Defense Department team reviewing the Cybersecurity Maturity Model Certification program met for the first time on Thursday, July 16, starting a 75-day clock that ends with a recommendations report in late September. DoD Chief Information Officer Kirsten Davies told reporters that day, after touring Kform, a small defense manufacturer in Sterling, Virginia, that the team has 60 days to gather feedback and review the program and another 15 days to deliver its recommendations to her and to Under Secretary of Defense for Acquisition and Sustainment Michael Duffey. Davies toured the plant with Small Business Administration Administrator Kelly Loeffler and Duffey, whose offices backed the July 13 suspension of CMMC Phase II third-party assessment requirements. SBA, in News Release 26-73, put certification costs at roughly $593,800 per firm requiring a third-party assessment and about $388,600 for firms eligible to self-assess, affecting more than 120,000 defense industrial base small businesses.
Background
CMMC was built to verify that defense contractors actually implement the security controls they have long been required to attest to. Level 1 covers federal contract information and relies on annual self-assessment against the 15 controls in FAR 52.204-21. Level 2 covers controlled unclassified information, keyed to the 110 controls in NIST SP 800-171 under DFARS 252.204-7012, and in its more demanding form requires an assessment by a certified third-party assessment organization, or C3PAO. Level 3 requires an assessment conducted by the Defense Industrial Base Cybersecurity Assessment Center, known as DIBCAC.
Phase II, under which third-party assessments were scheduled to become standard in many defense contracts, was set to begin November 10, 2026. The department suspended that phase on July 13 and stood up the review team now working against the late-September deadline. Per the Cyber AB, the program's accreditation body, nearly 2,000 defense contractors have already been certified at Level 2 and more than 1,000 assessors have been certified — firms and individuals that carried the cost of the program before the requirement was paused. Cyber AB CEO Matthew Travis said he was "both surprised and disappointed in yet another momentary pause."
Davies has been blunt about what she sees as the program's defect. She described CMMC assessments as a "burdensome, red-tape ridden, check-the-box, point-in-time view of a company's handling" of sensitive data, and said the department needs "to be thinking much more creatively, cleverly, and holistically." Loeffler framed it in small-business terms, saying "cybersecurity cannot come at the cost of bureaucracy that shuts out the very companies our warfighters depend on." Davies has not said whether third-party assessments survive the review.
Key Details
Three separate mechanisms are now running at once, and each carries a date contractors need on a calendar.
The first is the request for information. DoD posted "Reforming CMMC and Reducing Compliance Burden for the Defense Industrial Base (DIB)" on SAM.gov, with responses due by 12:00 pm ET on Friday, August 14, 2026. The notice asks industry to identify cost drivers and administrative burdens, name the specific security controls that deliver meaningful cyber uplift, describe how commercial cybersecurity tools and managed services could carry part of the load, detail the challenges firms hit with Phase I self-assessments, and propose policy reforms. Davies has said the review will examine "the totality of the Cybersecurity Maturity Model Certification program."
The second is the listening sessions. Davies said DoD will hold sessions across the country for defense contractors, "especially small and innovative companies," and separate sessions for the Cyber AB and the assessor community whose business model the review could reshape.
The third is contractual implementation. Duffey issued a memo directing program managers to produce amended requirements documents that strip Level 2 (C3PAO) and Level 3 (DIBCAC) requirements from active solicitations, with contracting officers issuing solicitation amendments as soon as practicable. For contracts already awarded with those requirements in them, contracting officers are directed to remove them by modification before exercising the next option period or during the next scheduled administrative modification. While the suspension holds, contracting officers may include only Level 1 (Self) or Level 2 (Self) requirements.
Davies framed the range of outcomes broadly, saying the review "could include everything from an overhaul to small tweaks here and there," while adding that what the department is "not going to do is death by a thousand cuts."
What It Means for Contractors
The assessment requirement is suspended. The underlying security obligations are not. FAR 52.204-21 still governs safeguarding of federal contract information. DFARS 252.204-7012 still requires implementation of the 110 controls in NIST SP 800-171, and Davies has said that clause, NIST 800-171 and CMMC Phase I all remain fully in place. A contractor that reads the suspension as permission to stop work on its system security plan or its plan of action and milestones is misreading it.
The enforcement exposure is unchanged and arguably sharper. Self-assessment scores are representations to the government, and inaccurate affirmations carry contractual and False Claims Act exposure. Removing the C3PAO checkpoint also removes the party that would have caught an inflated score before a contracting officer relied on it. That is worth sitting with: the suspension shifts risk from an auditor's desk onto the contractor's own attestation, which is the more expensive place for an error to surface.
For firms mid-assessment, the near-term decision is whether to pause C3PAO work or finish it. Nothing in the suspension invalidates a certification already earned, and nothing guarantees third-party assessment will not return in some form after September. Firms that have already sunk most of the cost have little to gain from stopping. Firms that have not started have a defensible reason to wait for the report.
For firms holding contracts that already carry Level 2 (C3PAO) or Level 3 requirements, the practical step is to raise the modification with the contracting officer rather than wait for it. Duffey's memo ties removal to the next option exercise or the next administrative modification, which for some contracts is months away. A contractor that flags the requirement early gets the relief early.
The RFI is the leverage point. The department is explicitly asking which controls are worth their cost and whether commercial tooling and managed services can substitute for bespoke compliance work — questions where a small manufacturer's operational experience carries more weight than a trade association's talking points. Responses close August 14, and the team has only 60 days to absorb what it receives before the report is due. Firms that want the September recommendations to reflect their actual cost structure should be drafting now, and should bring the same material to whichever listening session lands nearest to them.
Sources
- SBA Commends U.S. Department of War's Suspension of CMMC Phase II for Small Defense Contractors — SBA News Release 26-73
- Reforming CMMC and Reducing Compliance Burden for the Defense Industrial Base (DIB) — RFI, SAM.gov
- DoD plans CMMC listening sessions as questions swirl around review — Federal News Network
- Pentagon task force to review CMMC hits the ground running — DefenseScoop
- Department of War Suspends CMMC Phase II Requirements, but Cybersecurity Obligations Remain — Morgan Lewis
